Northern Virginia, USA
ProjectsOctober 22, 2025

LCPS Gift Card Phishing Incident Analysis (BEC Investigation)

LCPS Gift Card Phishing Incident Analysis (BEC Investigation) — project cover
This project documents a real-world phishing incident that targeted my Loudoun County Public Schools (LCPS) email account and escalated into a gift card scam via SMS — a classic Business Email Compromise (BEC) attack pattern. Instead of ignoring the attempt, I treated it as a SOC-style incident investigation, collecting evidence, performing email header forensics, analyzing social engineering tactics, and documenting the full incident response lifecycle aligned with industry frameworks. Why this matters:
Phishing and BEC attacks remain one of the most common and costly threats facing organizations today. This case study demonstrates how analysts investigate suspicious messages, validate sender authenticity, and prevent financial loss through technical analysis, documentation, and awareness.
  • Date: October 22, 2025
  • Target: LCPS Substitute Teacher email account
  • Initial Vector: Email titled “Weekly Operations Review”
  • Escalation: SMS messages requesting urgent gift card purchases
  • Objective: Financial theft via social engineering
The attacker impersonated an LCPS supervisor using a generic Outlook.com email address, requested confidentiality, and attempted to pressure immediate action — all hallmark indicators of a BEC gift card scam.
  • Collected the original phishing email and follow-up SMS messages.
  • Redacted sensitive personal information to prevent data exposure.
  • Preserved original artifacts (email headers, screenshots) to maintain integrity and chain-of-custody.
  • Extracted full message headers from Microsoft Outlook.
  • Analyzed:
    • From and Return-Path fields
    • SPF, DKIM, and DMARC authentication results
    • Received mail server chain
  • Verified the email originated from an external Outlook.com domain, not LCPS infrastructure.
  • Built a custom Python script (header_quickcheck.py) to:
    • Parse raw email headers using regex
    • Extract SPF/DKIM/DMARC results
    • Highlight external domains and authentication mismatches
  • Demonstrated how lightweight tooling can assist analysts during triage.
Identified multiple manipulation techniques:
  • Authority: Impersonation of a supervisor figure
  • Urgency: Pressure to act immediately
  • Confidentiality: Requests to avoid verification
  • Financial Lure: Gift card purchase request
  • Did not engage further with the attacker.
  • Reported the incident to LCPS IT security.
  • Blocked the associated phone number and email address.
  • Documented findings in a formal technical report and infographic.
  • NIST SP 800-61 (Incident Response Lifecycle):
    • Detection & Analysis
    • Containment
    • Reporting
  • MITRE ATT&CK (Enterprise):
    • T1566 – Phishing
    • T1656 – Financial Theft
Mapping the incident to established frameworks demonstrates how real-world phishing attempts fit into standardized security models used in SOC environments.
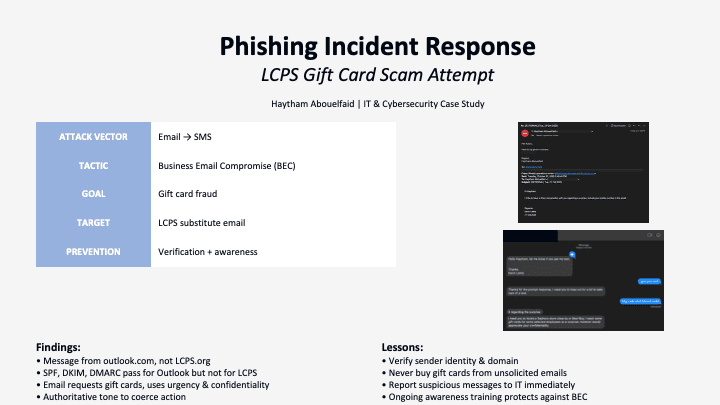
  • Created a 1-page phishing case study poster summarizing:
    • Attack vector (Email → SMS)
    • BEC tactics used
    • Technical findings
    • Prevention strategies
  • Designed for clear communication to both technical and non-technical audiences.
For the complete technical breakdown — including raw email header extraction, SPF/DKIM/DMARC validation, sender IP tracing, and framework alignment — view the full investigation document below: 📄 Phishing Analysis Report (Full Word Document):
👉 https://docs.google.com/document/d/1knII0QkWs1Ocrp-s3WhjqP3S7O1F64kj/edit?usp=sharing
This report includes:
  • Full email header analysis
  • Authentication result interpretation
  • Social engineering breakdown table
  • NIST SP 800-61 lifecycle mapping
  • MITRE ATT&CK alignment
  • Formal incident documentation
  • Email Platform: Microsoft Outlook (message source & headers)
  • Header Analysis: MXToolbox
  • Programming: Python (regex-based header parsing)
  • Documentation: Markdown, technical incident report
  • Visualization: PowerPoint (infographic poster)
  • Version Control: Git & GitHub
  • Email authentication checks (SPF/DKIM/DMARC) must be paired with contextual analysis — passing checks alone do not guarantee legitimacy.
  • BEC attacks rely heavily on human trust and urgency, not malware.
  • Proper documentation and reporting are critical components of effective incident response.
  • Turning real incidents into structured case studies accelerates hands-on cybersecurity learning.
  • Successfully identified and contained a real phishing attempt with no financial or data loss.
  • Produced a complete SOC-style investigation artifact set:
    • Evidence
    • Header analysis
    • Python tooling
    • Framework mapping
    • Visual reporting
  • Published the project to GitHub and LinkedIn as part of a professional cybersecurity portfolio.
Next steps:
  • Extend the header analysis script with threat-intel enrichment.
  • Add phishing detection heuristics for automated flagging.
  • Incorporate the project into a broader phishing awareness training module.
Related projects

Sentilops – Financial Intelligence Automation System

Sentilops – Financial Intelligence Automation System

Built an AI-assisted finance-intelligence pipeline that ingests newsletters and business content, extracts structured signals, routes actions, stores knowledge, and alerts on relevant financial and cash-flow insights.
NOVA CASHFLOW – Financial Literacy Community Automation

NOVA CASHFLOW – Financial Literacy Community Automation

Built community, research, newsletter, and financial-intelligence workflows supporting NOVA CASHFLOW's practical financial-literacy mission for students and young professionals.
Finance + Real Estate Intelligence Automation Suite

Finance + Real Estate Intelligence Automation Suite

A reusable automation architecture for extracting, classifying, storing, and routing finance and real-estate intelligence from newsletters, research sources, and business content.
SentinelOps – AI-Assisted Phishing Investigation Platform

SentinelOps – AI-Assisted Phishing Investigation Platform

Built a Python-based phishing investigation platform that automates webpage evidence collection, IOC extraction, phishing risk scoring, and analyst-ready reporting using Playwright, OpenRouter, and SQLite.
SmishGuard – USPS Smishing Detection & IOC Extraction

SmishGuard – USPS Smishing Detection & IOC Extraction

Analyzed a real-world USPS SMS phishing campaign and developed a Python-based CLI tool to automate smishing triage, extract indicators of compromise (IOCs), generate incident response documentation, and create detection rules.
Enterprise Help Desk Lab – osTicket on Microsoft Azure

Enterprise Help Desk Lab – osTicket on Microsoft Azure

Deployed and secured a cloud-hosted enterprise help desk system in Microsoft Azure using Ubuntu, Apache, MySQL, and osTicket. Implemented SLA tiers, department-based routing, structured triage workflows, and simulated enterprise IT operations.
CupidSecure – AI-Powered Romance Scam Detection

CupidSecure – AI-Powered Romance Scam Detection

Built an end-to-end AI security platform that analyzes dating conversations for romance-scam patterns, scores financial risk, and provides a training simulator and threat dashboard — winner of 1st Place in the Blockchain, Cyber & Security track at HackFax × PatriotHacks 2026.
LinkedIn Content Automation Engine (Make.com, OpenRouter, Gamma AI)

LinkedIn Content Automation Engine (Make.com, OpenRouter, Gamma AI)

Built an end-to-end LinkedIn content engine that turns TLDR newsletters into SOC-focused posts with AI-generated Gamma slide decks, fully automated and scheduled in Make.com.
Cybersecurity Awareness Research for College Students

Cybersecurity Awareness Research for College Students

Transformed an ENG 111 research assignment into a real-world cybersecurity policy proposal advocating mandatory student cybersecurity training and continuous awareness initiatives, supported by peer-reviewed research.
SOAR + EDR Automated Incident Response (LimaCharlie, Tines, Slack, HTML Email)

SOAR + EDR Automated Incident Response (LimaCharlie, Tines, Slack, HTML Email)

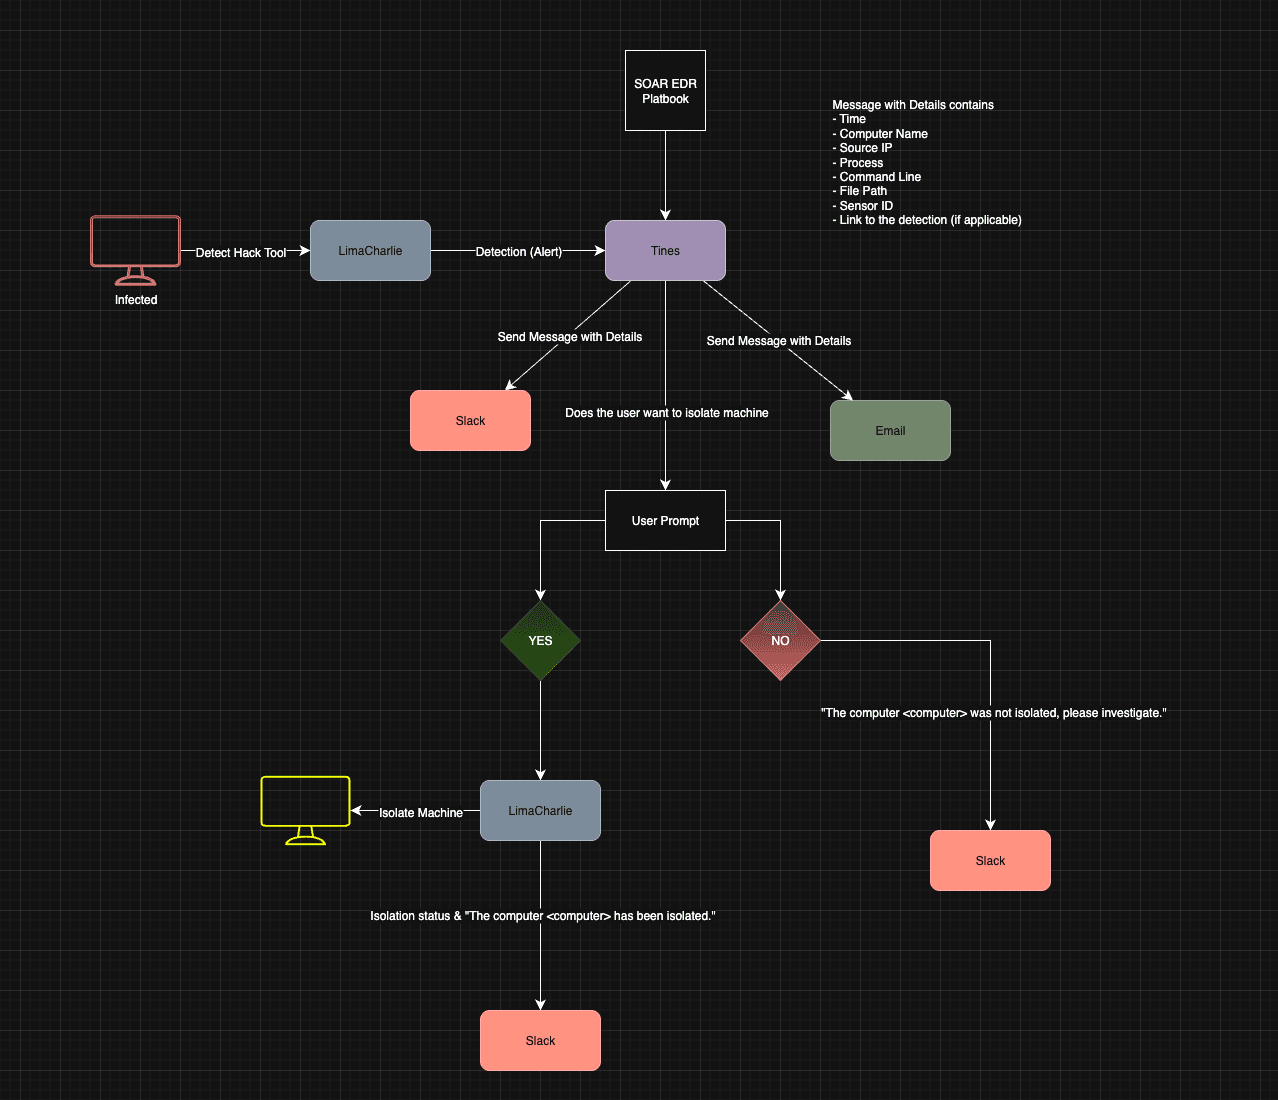
Developed a fully automated detection-to-isolation workflow: LimaCharlie detects suspicious activity, Tines generates Slack and email alerts, collects analyst approval, and isolates the endpoint via API—confirming success in Slack.
Active Directory 2.0: SIEM + SOAR Auto-Response (Splunk, Slack, Shuffle)

Active Directory 2.0: SIEM + SOAR Auto-Response (Splunk, Slack, Shuffle)

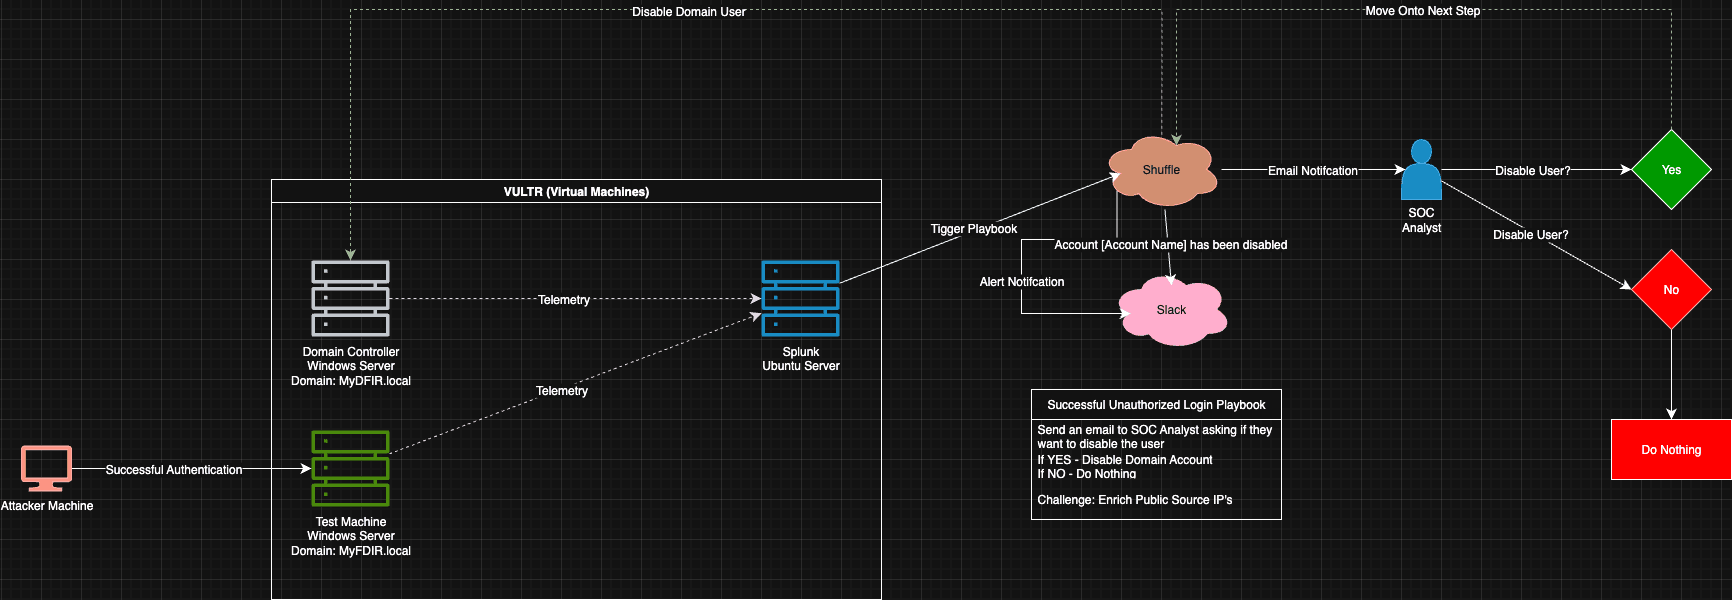
Built an end-to-end detection-to-response pipeline: Splunk detects unauthorized successful RDP logins, Shuffle collects analyst approval by email, then disables the domain account in AD via LDAP and confirms in Slack.
Cloud SOC Honeypot: Microsoft Sentinel Attack Map (Azure)

Cloud SOC Honeypot: Microsoft Sentinel Attack Map (Azure)

Built a cloud-based SOC lab: deployed a Windows honeypot VM in Azure, captured 44,000+ brute-force attempts, forwarded logs to Log Analytics, integrated with Microsoft Sentinel, enriched attacker IPs with GeoIP, and visualized global attack sources on a live map.
Windows Recovery Project: BIOS Boot Failure (Error 1962)

Windows Recovery Project: BIOS Boot Failure (Error 1962)

Troubleshot and restored a compromised Windows desktop that failed with BIOS Error 1962: 'No Operating System Found.' Adjusted BIOS boot configuration, attempted DISM/SFC repairs, then performed a clean OS reinstall via bootable USB to recover full functionality.
IntelliPath AI: Personalized Learning Through AI-Driven Video Summaries

IntelliPath AI: Personalized Learning Through AI-Driven Video Summaries

Developing an AI-powered platform that transforms YouTube videos into structured summaries, actionable notes, and personalized learning paths. Features include transcript analysis, AI assistant chat, sidebar navigation with history/folders, payment integration, and cloud-based persistence.
Astray: Lost Kingdoms (Python Pixel RPG)

Astray: Lost Kingdoms (Python Pixel RPG)

Building a 16-bit RPG in Python using Pygame, featuring interactive menus, real-time cutscenes, object-oriented game logic, and a story-driven quest system. Demonstrates software development skills, creativity, and iterative project management.