Northern Virginia, USA
ProjectsApril 4, 2026

SentinelOps – AI-Assisted Phishing Investigation Platform

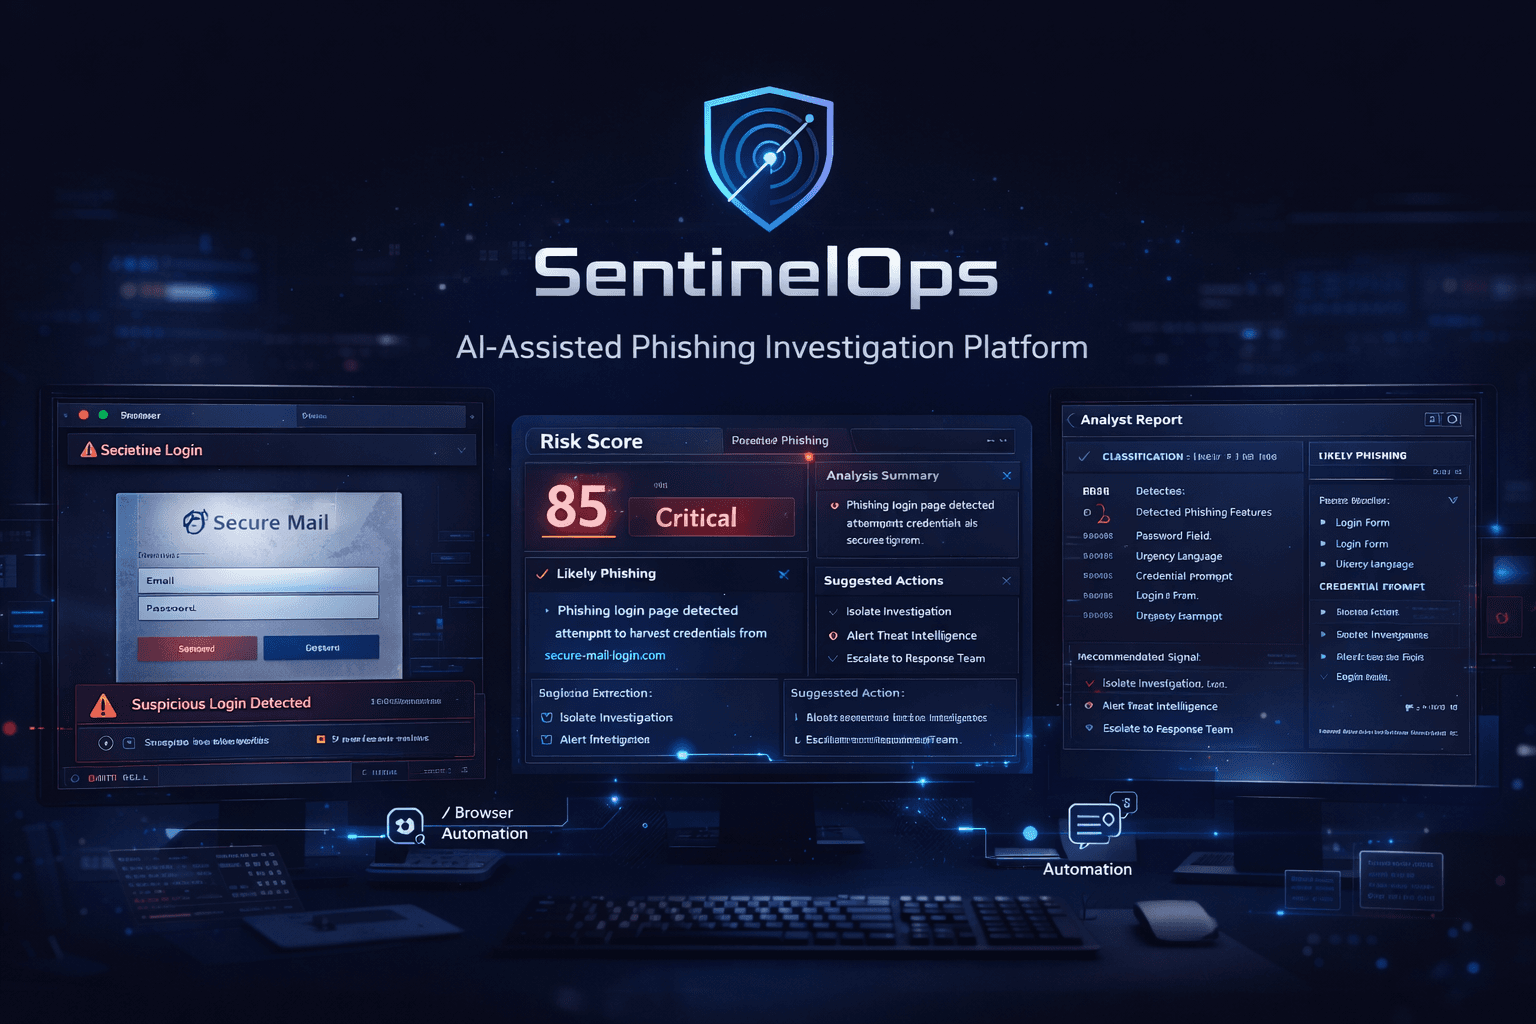
SentinelOps – AI-Assisted Phishing Investigation Platform — project cover
SentinelOps is an AI-assisted phishing investigation platform designed to automate the early stages of suspicious webpage triage. Phishing investigations typically require analysts to manually:
  • open suspicious URLs in a controlled environment
  • capture screenshots and rendered HTML
  • extract indicators of compromise (IOCs)
  • identify phishing signals
  • document findings in a structured report
To simulate and automate this workflow, I built SentinelOps as a CLI-based cybersecurity tool that combines browser automation, deterministic detection logic, and LLM-assisted analysis.
SentinelOps Banner SentinelOps models a real SOC-style phishing investigation workflow, transforming a suspicious URL into structured, analyst-ready outputs.
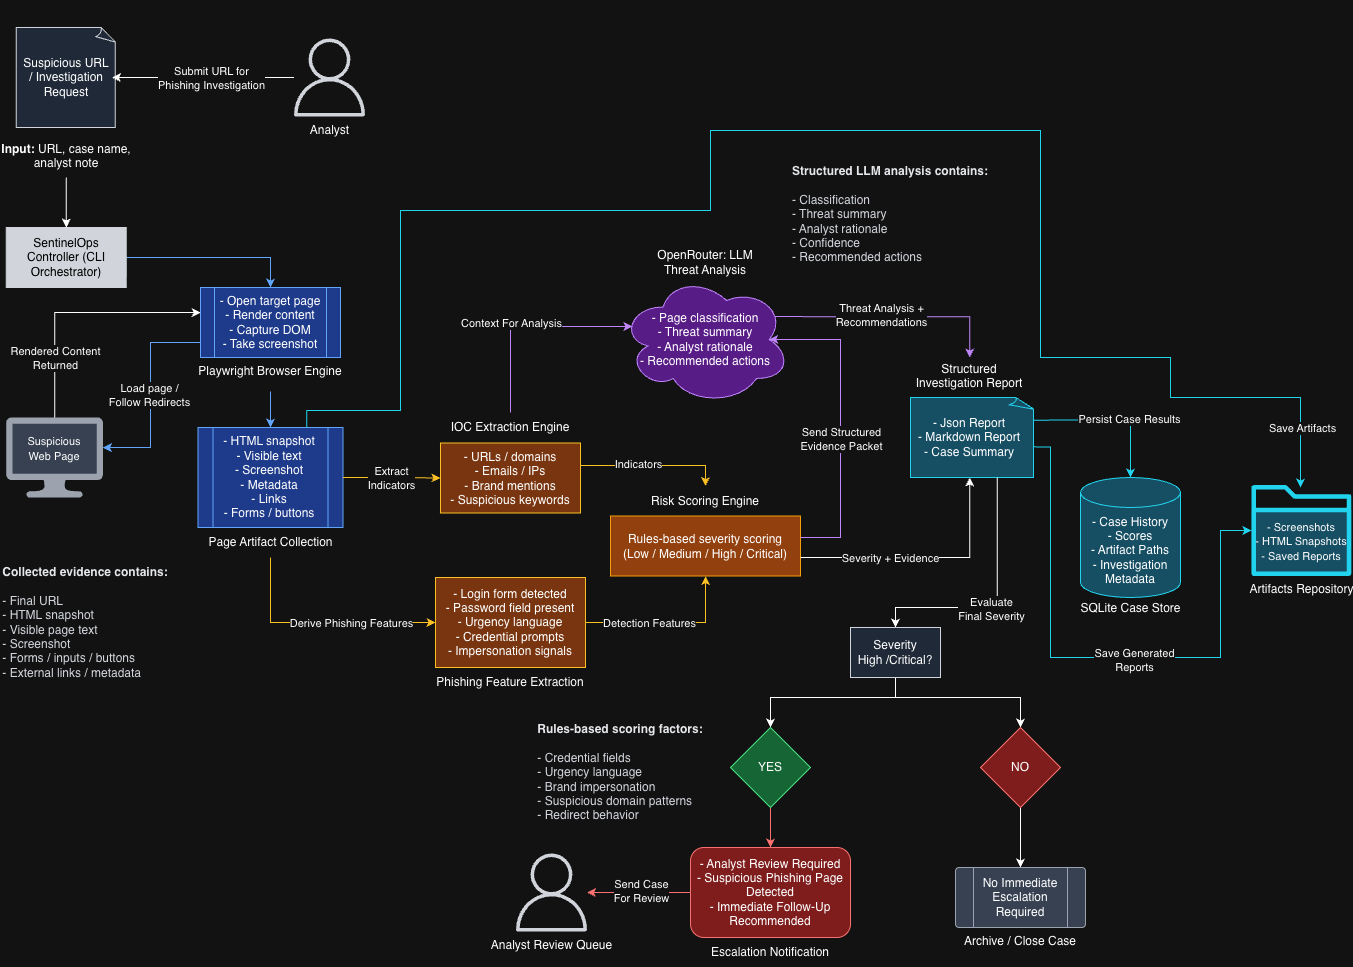
SentinelOps Architecture Workflow The platform follows a modular pipeline:
  • Analyst submits a suspicious URL
  • Browser automation collects rendered webpage artifacts
  • Indicators of compromise are extracted
  • Phishing detection features are derived
  • A deterministic risk score is calculated
  • LLM generates structured analysis
  • Reports are created and stored
  • Case data is persisted in SQLite
This architecture ensures explainability, modularity, and real-world applicability.
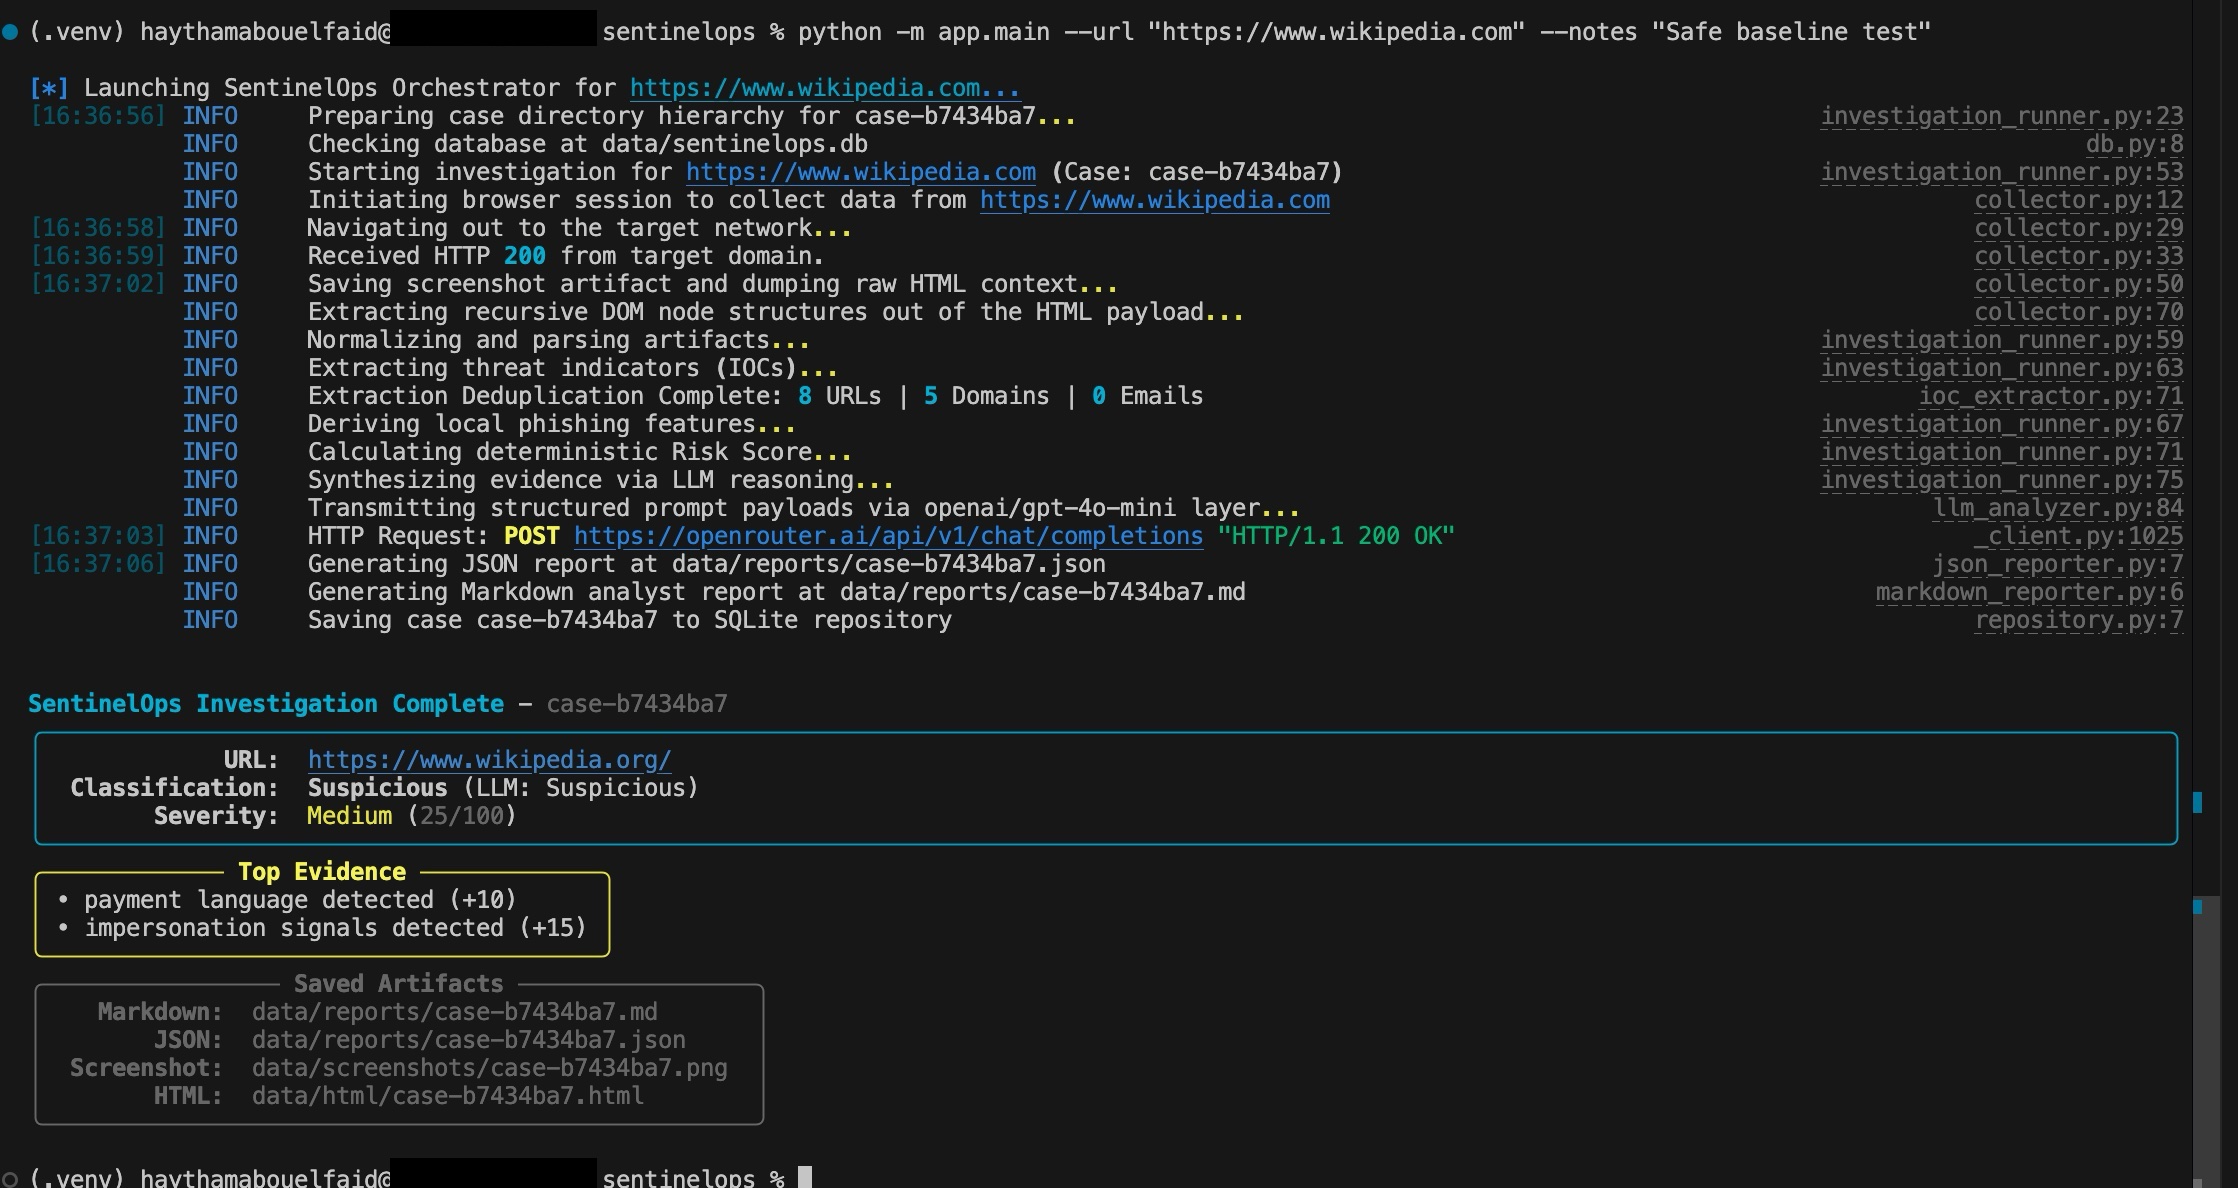
SentinelOps Terminal Run SentinelOps is operated through a command-line interface: python -m app.main --url "https://example.com" --notes "Investigation test" During execution, the system:
  • launches a browser session
  • captures HTML and screenshots
  • extracts IOCs
  • derives phishing indicators
  • calculates a risk score
  • generates structured reports
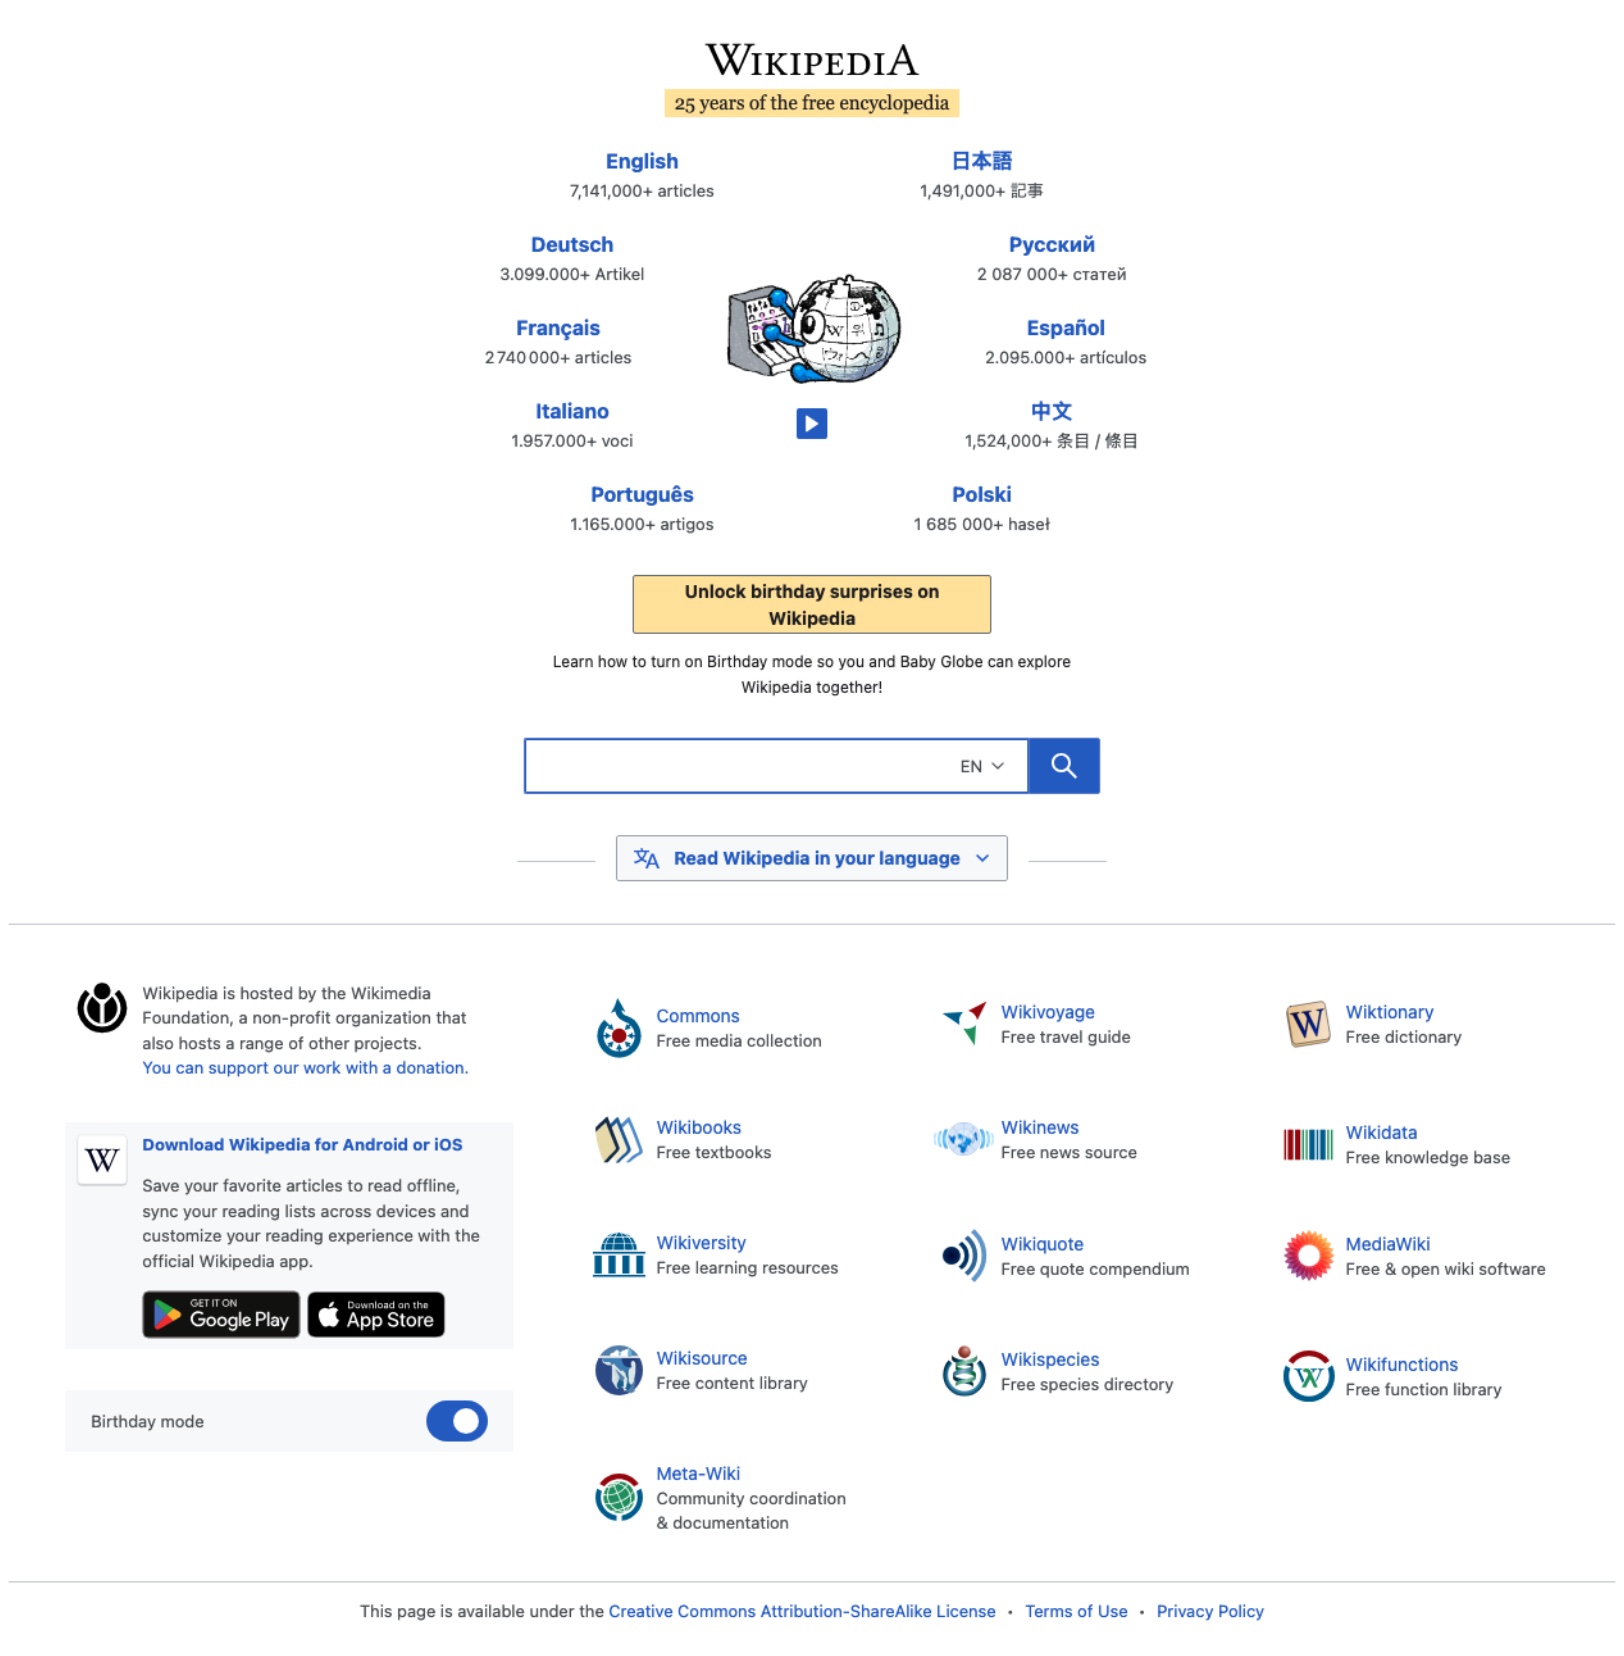
Browser Artifact Screenshot Using Playwright, SentinelOps captures:
  • Full-page screenshot
  • Rendered HTML snapshot
  • Visible text
  • Forms and input fields
  • Buttons and links
  • Page metadata
This approach mirrors how a real analyst would inspect a suspicious webpage.
SentinelOps extracts key indicators of compromise:
  • URLs
  • Domains
  • Email addresses
  • IP addresses
  • Suspicious keywords
  • Brand mentions
It then derives phishing-specific signals such as:
  • login form presence
  • credential prompts
  • urgency language
  • payment-related language
  • impersonation indicators
  • suspicious domain patterns
This deterministic logic improves consistency and explainability compared to AI-only approaches.
SentinelOps assigns a deterministic phishing risk score (0–100) based on detected indicators. Severity levels include:
  • Low
  • Medium
  • High
  • Critical
Each score is backed by explicit evidence, allowing analysts to understand why a page was flagged.
SentinelOps integrates OpenRouter to generate structured analysis based on collected evidence. The LLM produces:
  • Classification
  • Threat summary
  • Analyst rationale
  • Confidence level
  • Recommended actions
The LLM is used as a supporting analysis layer, not as the primary detection engine.
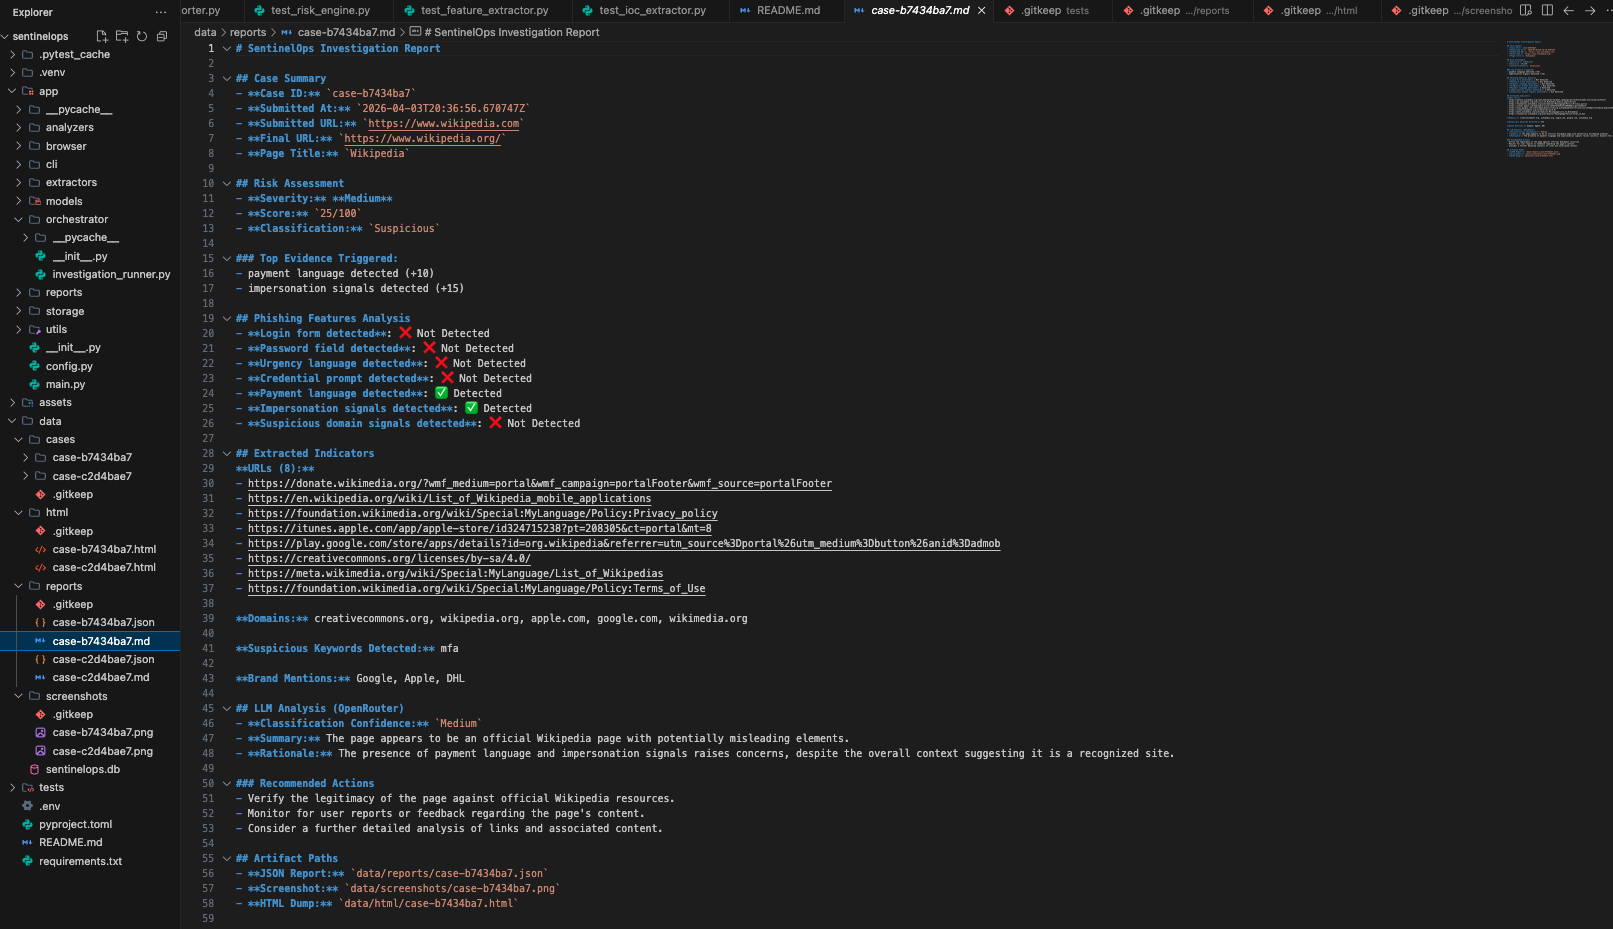
Markdown Report Provides a human-readable investigation summary including:
  • case details
  • detected indicators
  • phishing features
  • severity classification
  • recommended actions
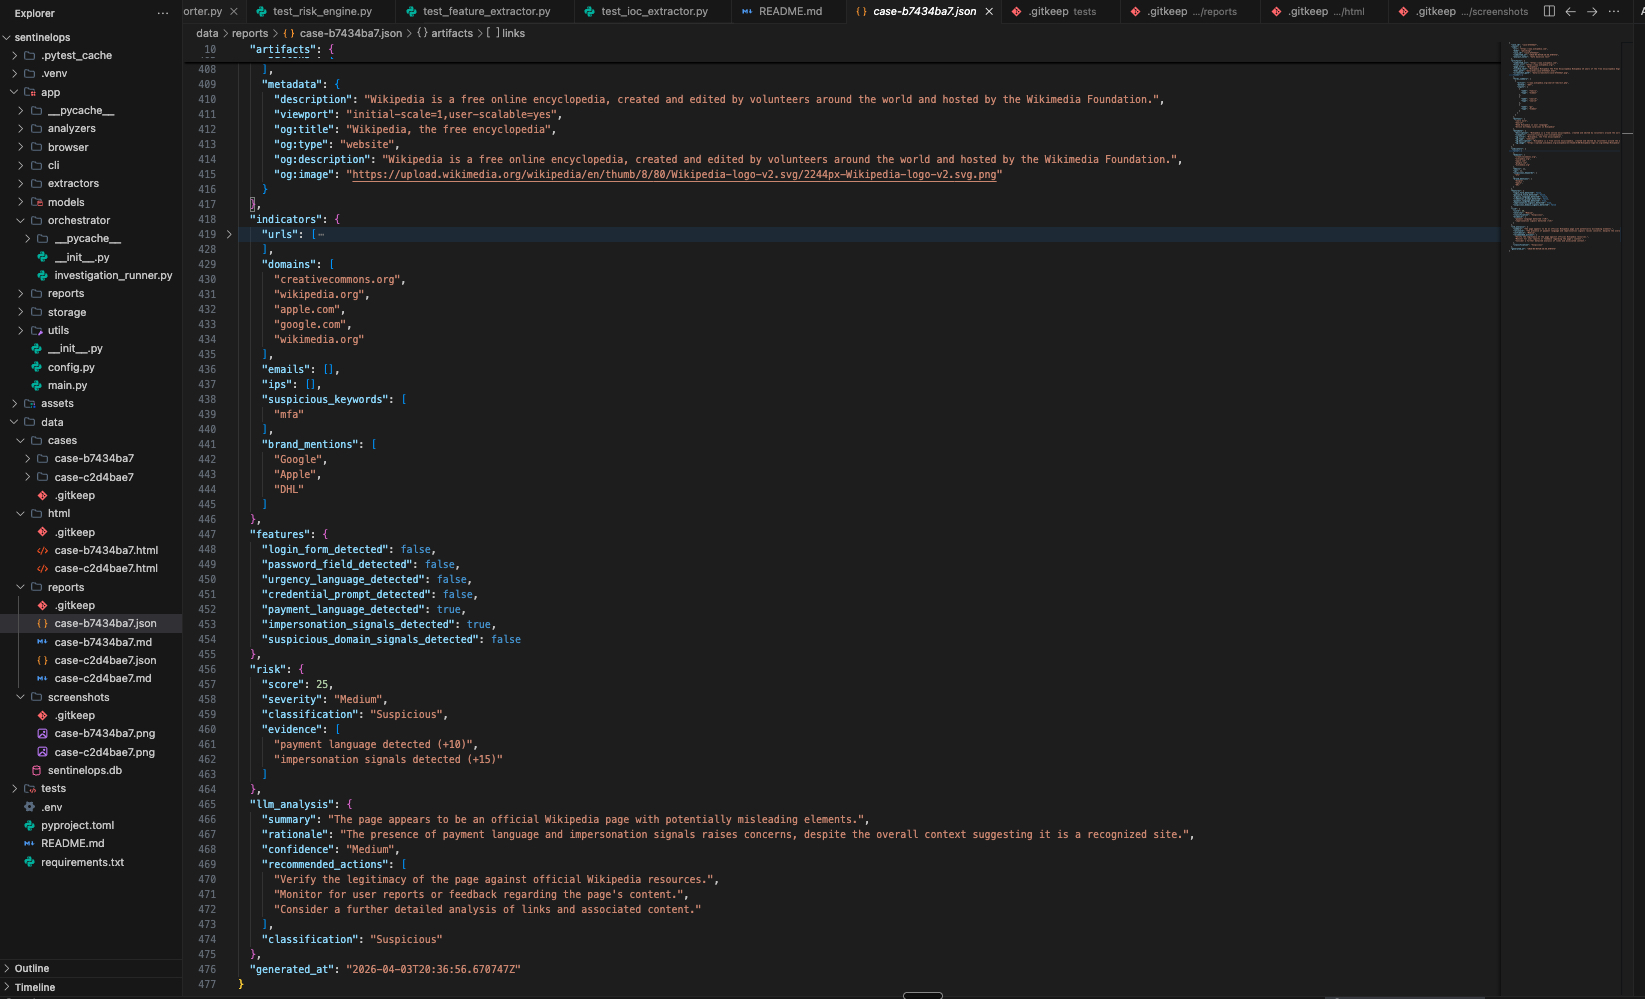
JSON Report Machine-readable output containing:
  • extracted indicators
  • detection features
  • risk score
  • LLM analysis
  • investigation metadata
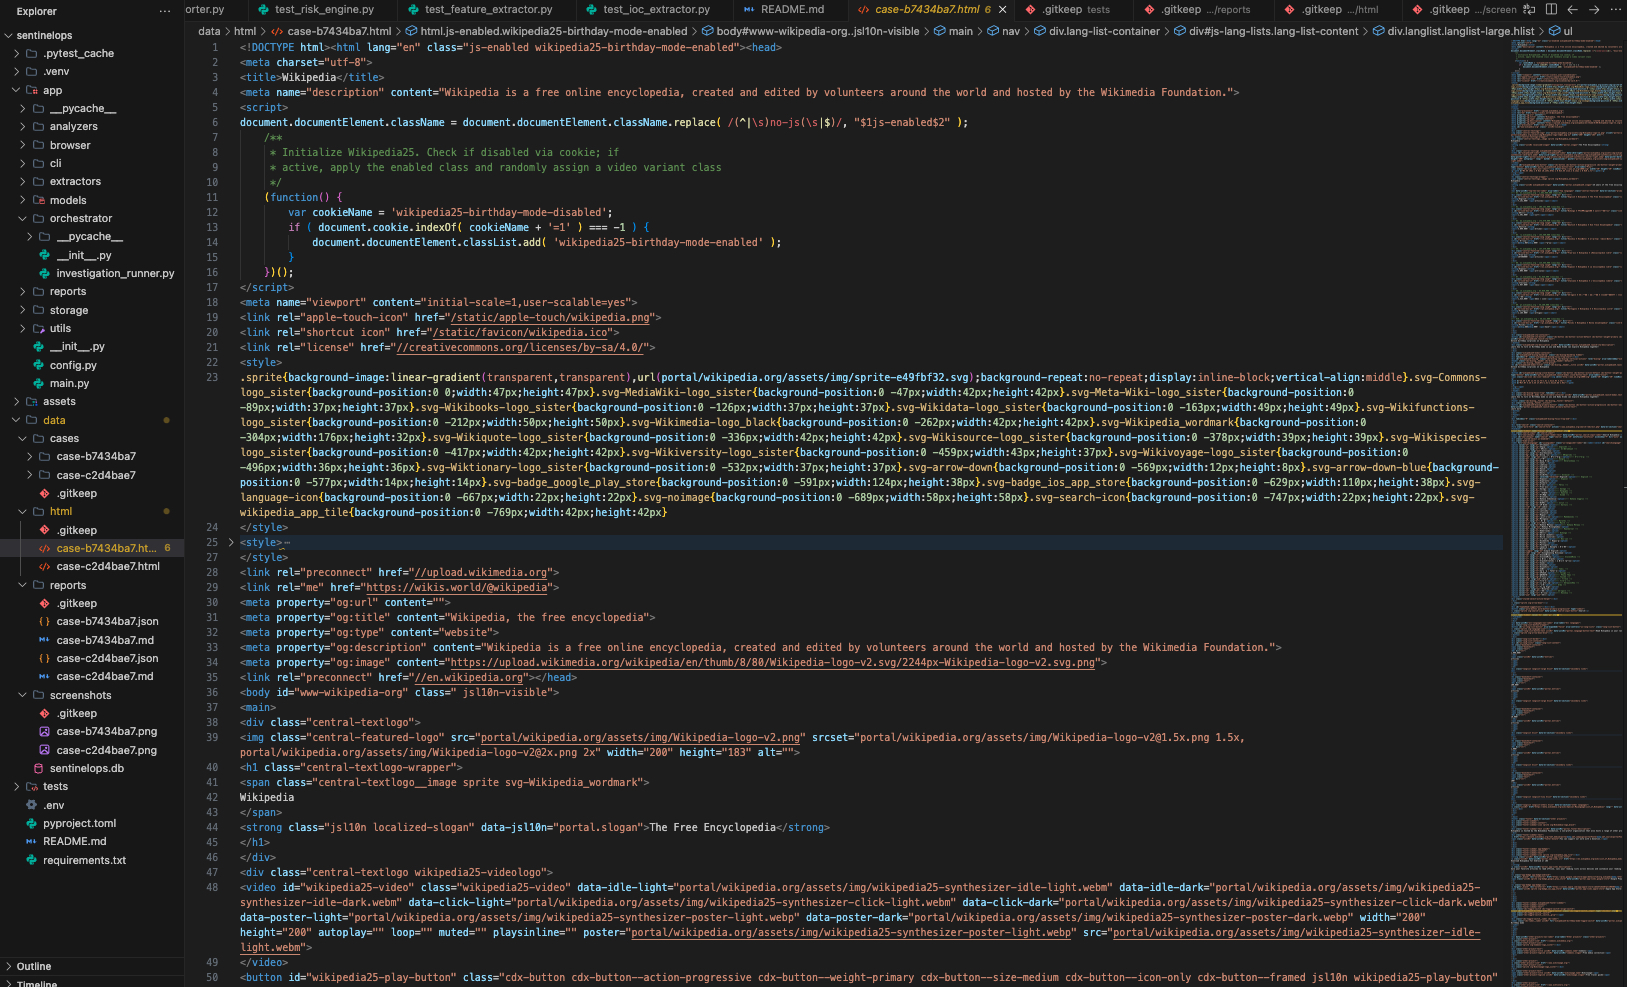
HTML Snapshot Stores the full rendered HTML for:
  • offline analysis
  • evidence preservation
  • forensic review
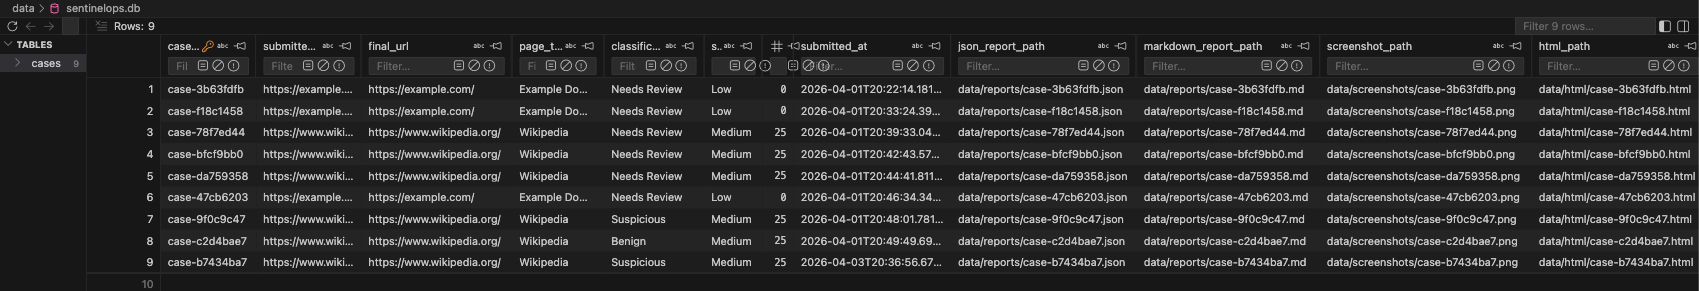
SQLite Case Store Each investigation is stored in a SQLite database, including:
  • case ID
  • URL
  • classification
  • severity
  • report paths
  • artifact locations
This simulates a lightweight SOC case management system.
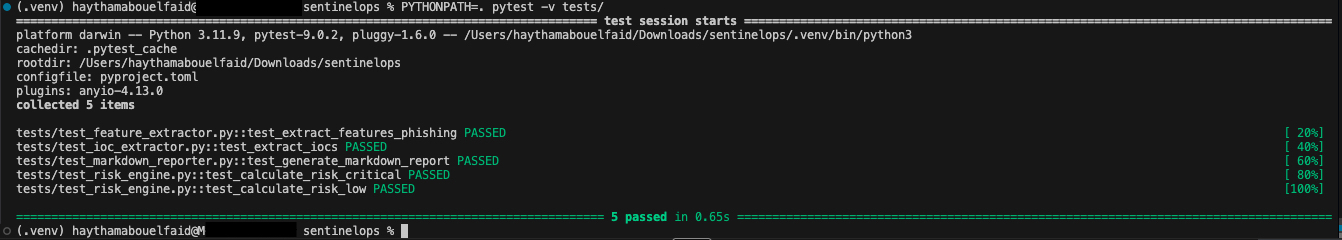
Test Suite Pass SentinelOps includes automated testing using pytest to validate:
  • IOC extraction
  • phishing feature detection
  • risk scoring logic
  • report generation
All core detection components are tested to ensure reliability and consistency.
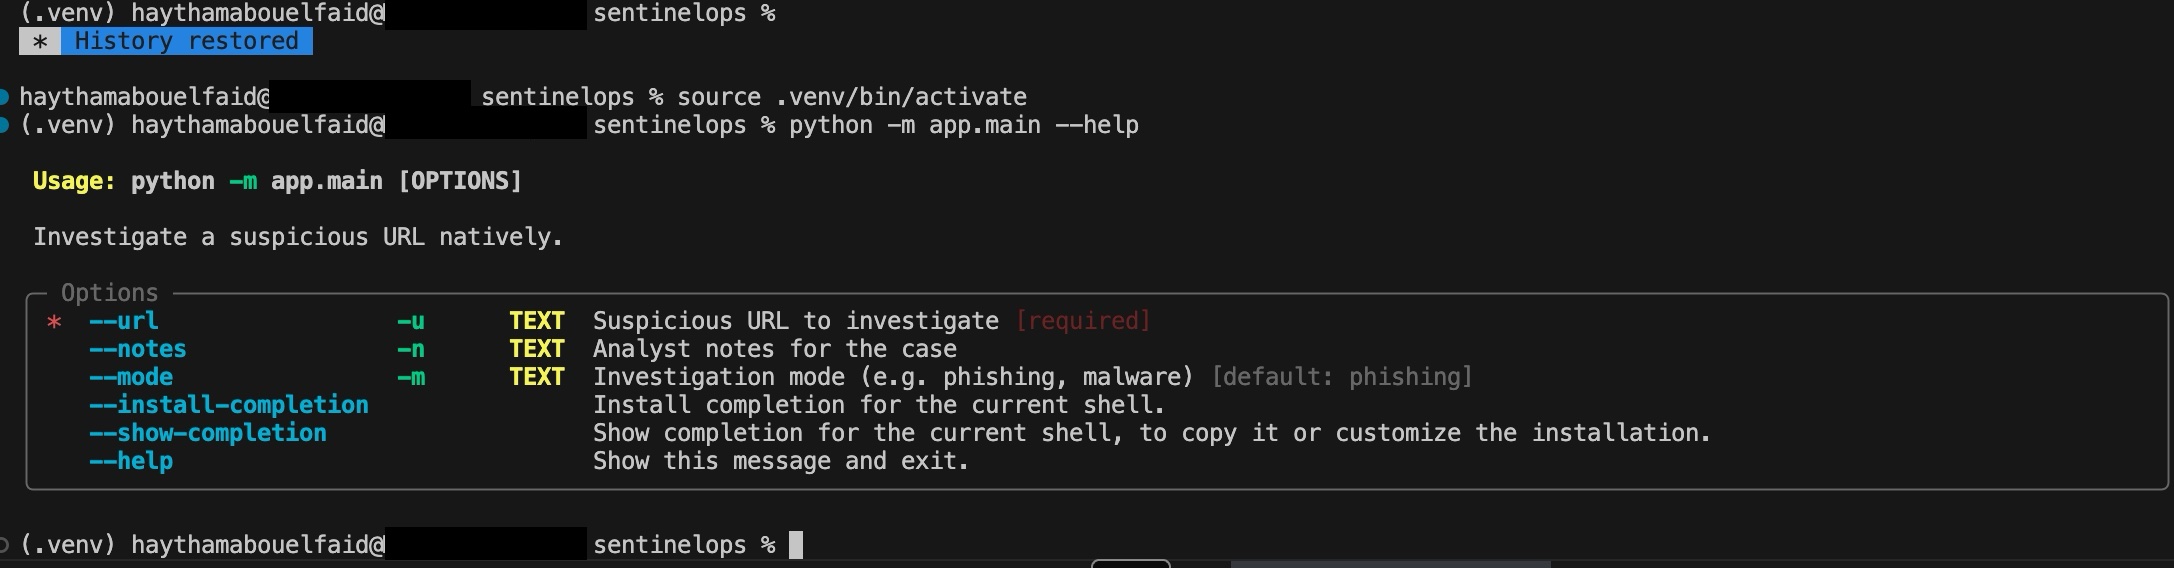
CLI Help Output The CLI provides a simple interface for running investigations with options for:
  • URL input
  • analyst notes
  • investigation mode
Security & Detection
  • Phishing analysis
  • IOC extraction
  • Threat detection logic
  • Risk scoring
Development
  • Python
  • Playwright
  • BeautifulSoup
  • Typer CLI
  • Pydantic
AI Integration
  • OpenRouter
Data & Storage
  • SQLite
Testing
  • pytest
  • Built a full phishing investigation pipeline from scratch
  • Automated browser-based evidence collection
  • Developed deterministic detection and scoring logic
  • Integrated LLM-assisted structured analysis
  • Generated analyst-ready and machine-readable reports
  • Implemented persistent case tracking with SQLite
  • Validated core functionality with automated testing
This project demonstrates practical experience in phishing investigation, security automation, detection engineering, and AI-assisted cybersecurity workflows.
GitHub Repository:
https://github.com/HaythamAbouelfaid/SentinelOps
Related projects

Sentilops – Financial Intelligence Automation System

Sentilops – Financial Intelligence Automation System

Built an AI-assisted finance-intelligence pipeline that ingests newsletters and business content, extracts structured signals, routes actions, stores knowledge, and alerts on relevant financial and cash-flow insights.
NOVA CASHFLOW – Financial Literacy Community Automation

NOVA CASHFLOW – Financial Literacy Community Automation

Built community, research, newsletter, and financial-intelligence workflows supporting NOVA CASHFLOW's practical financial-literacy mission for students and young professionals.
Finance + Real Estate Intelligence Automation Suite

Finance + Real Estate Intelligence Automation Suite

A reusable automation architecture for extracting, classifying, storing, and routing finance and real-estate intelligence from newsletters, research sources, and business content.
SmishGuard – USPS Smishing Detection & IOC Extraction

SmishGuard – USPS Smishing Detection & IOC Extraction

Analyzed a real-world USPS SMS phishing campaign and developed a Python-based CLI tool to automate smishing triage, extract indicators of compromise (IOCs), generate incident response documentation, and create detection rules.
Enterprise Help Desk Lab – osTicket on Microsoft Azure

Enterprise Help Desk Lab – osTicket on Microsoft Azure

Deployed and secured a cloud-hosted enterprise help desk system in Microsoft Azure using Ubuntu, Apache, MySQL, and osTicket. Implemented SLA tiers, department-based routing, structured triage workflows, and simulated enterprise IT operations.
CupidSecure – AI-Powered Romance Scam Detection

CupidSecure – AI-Powered Romance Scam Detection

Built an end-to-end AI security platform that analyzes dating conversations for romance-scam patterns, scores financial risk, and provides a training simulator and threat dashboard — winner of 1st Place in the Blockchain, Cyber & Security track at HackFax × PatriotHacks 2026.
LinkedIn Content Automation Engine (Make.com, OpenRouter, Gamma AI)

LinkedIn Content Automation Engine (Make.com, OpenRouter, Gamma AI)

Built an end-to-end LinkedIn content engine that turns TLDR newsletters into SOC-focused posts with AI-generated Gamma slide decks, fully automated and scheduled in Make.com.
Cybersecurity Awareness Research for College Students

Cybersecurity Awareness Research for College Students

Transformed an ENG 111 research assignment into a real-world cybersecurity policy proposal advocating mandatory student cybersecurity training and continuous awareness initiatives, supported by peer-reviewed research.
SOAR + EDR Automated Incident Response (LimaCharlie, Tines, Slack, HTML Email)

SOAR + EDR Automated Incident Response (LimaCharlie, Tines, Slack, HTML Email)

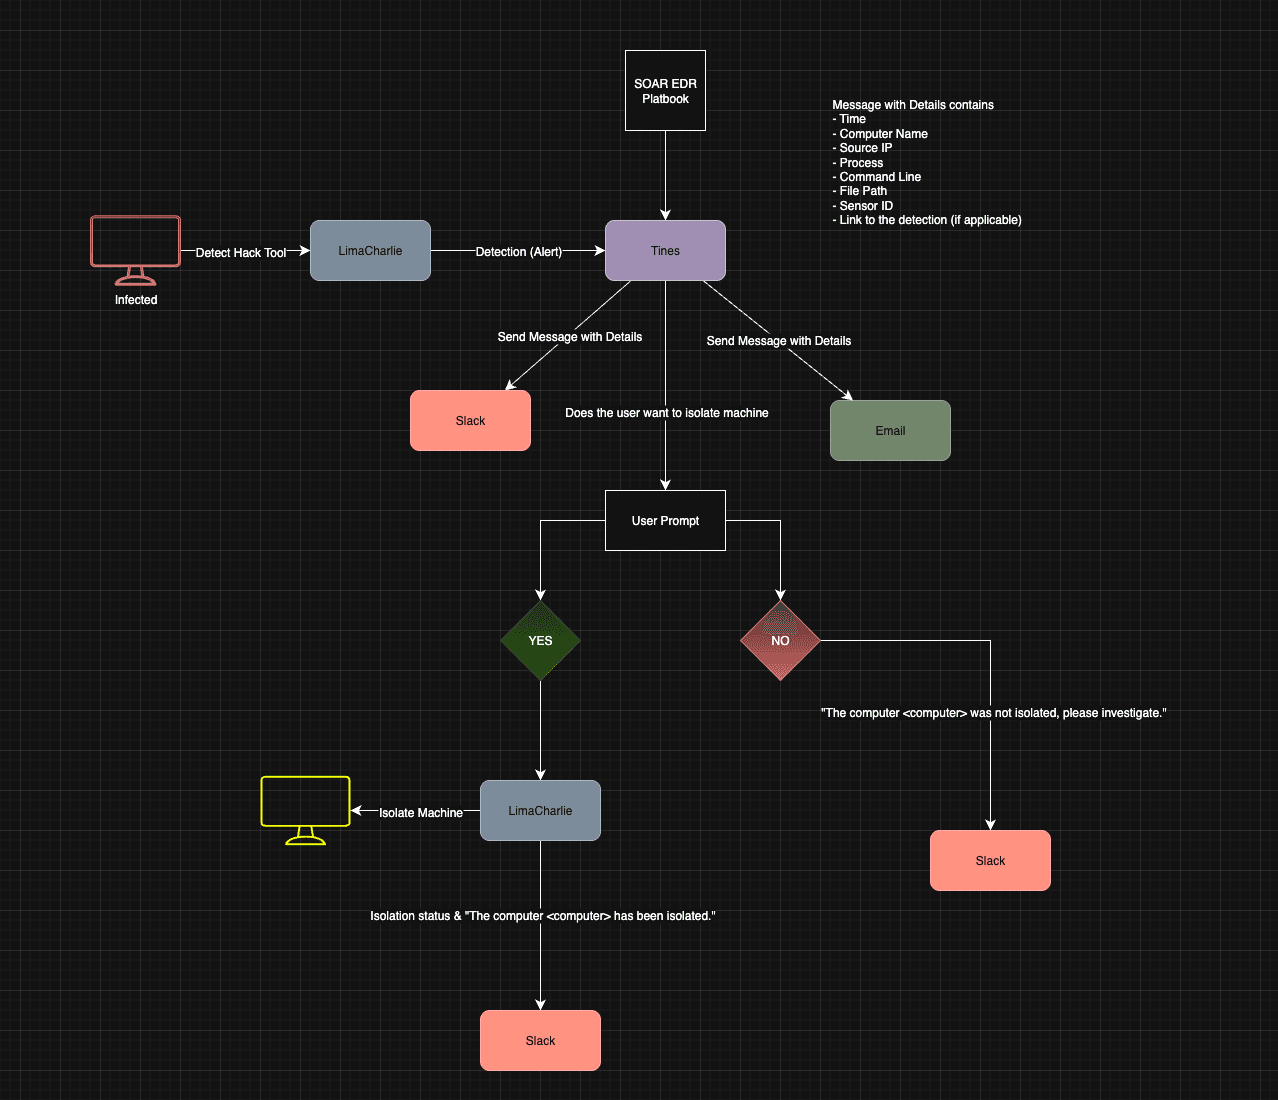
Developed a fully automated detection-to-isolation workflow: LimaCharlie detects suspicious activity, Tines generates Slack and email alerts, collects analyst approval, and isolates the endpoint via API—confirming success in Slack.
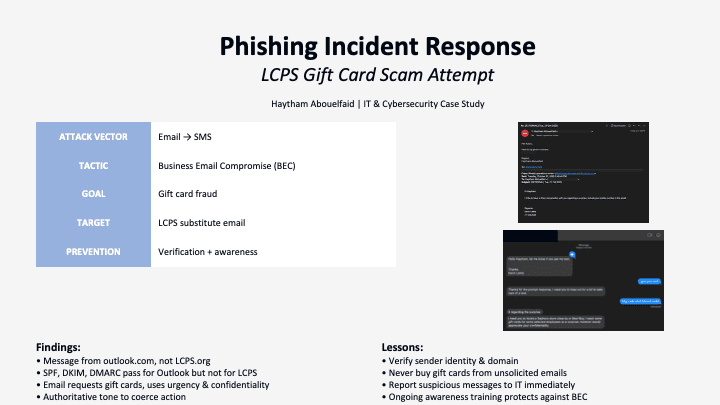
LCPS Gift Card Phishing Incident Analysis (BEC Investigation)

LCPS Gift Card Phishing Incident Analysis (BEC Investigation)

Investigated and documented a real-world Business Email Compromise (BEC) phishing attempt targeting an LCPS email account. Performed email header forensics, social engineering analysis, framework mapping, and produced a formal incident report and visual case-study poster.
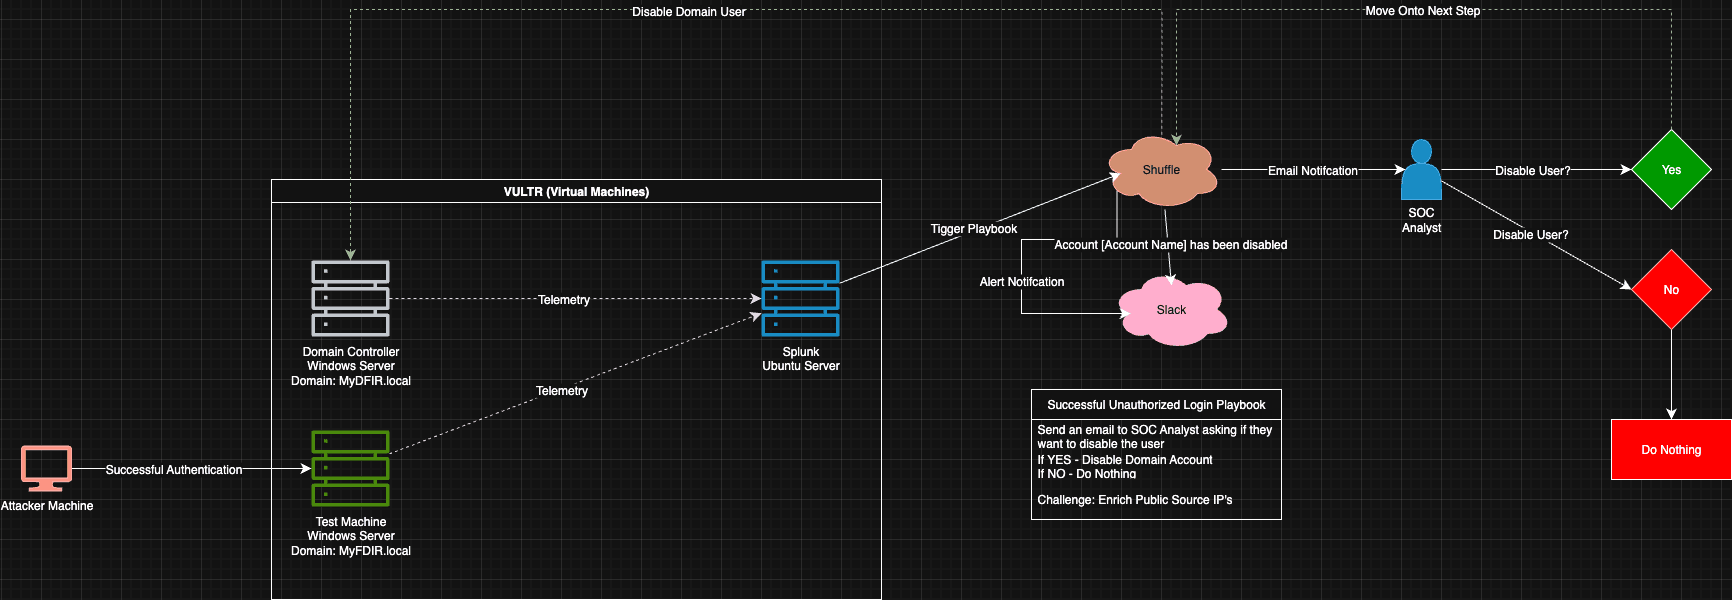
Active Directory 2.0: SIEM + SOAR Auto-Response (Splunk, Slack, Shuffle)

Active Directory 2.0: SIEM + SOAR Auto-Response (Splunk, Slack, Shuffle)

Built an end-to-end detection-to-response pipeline: Splunk detects unauthorized successful RDP logins, Shuffle collects analyst approval by email, then disables the domain account in AD via LDAP and confirms in Slack.
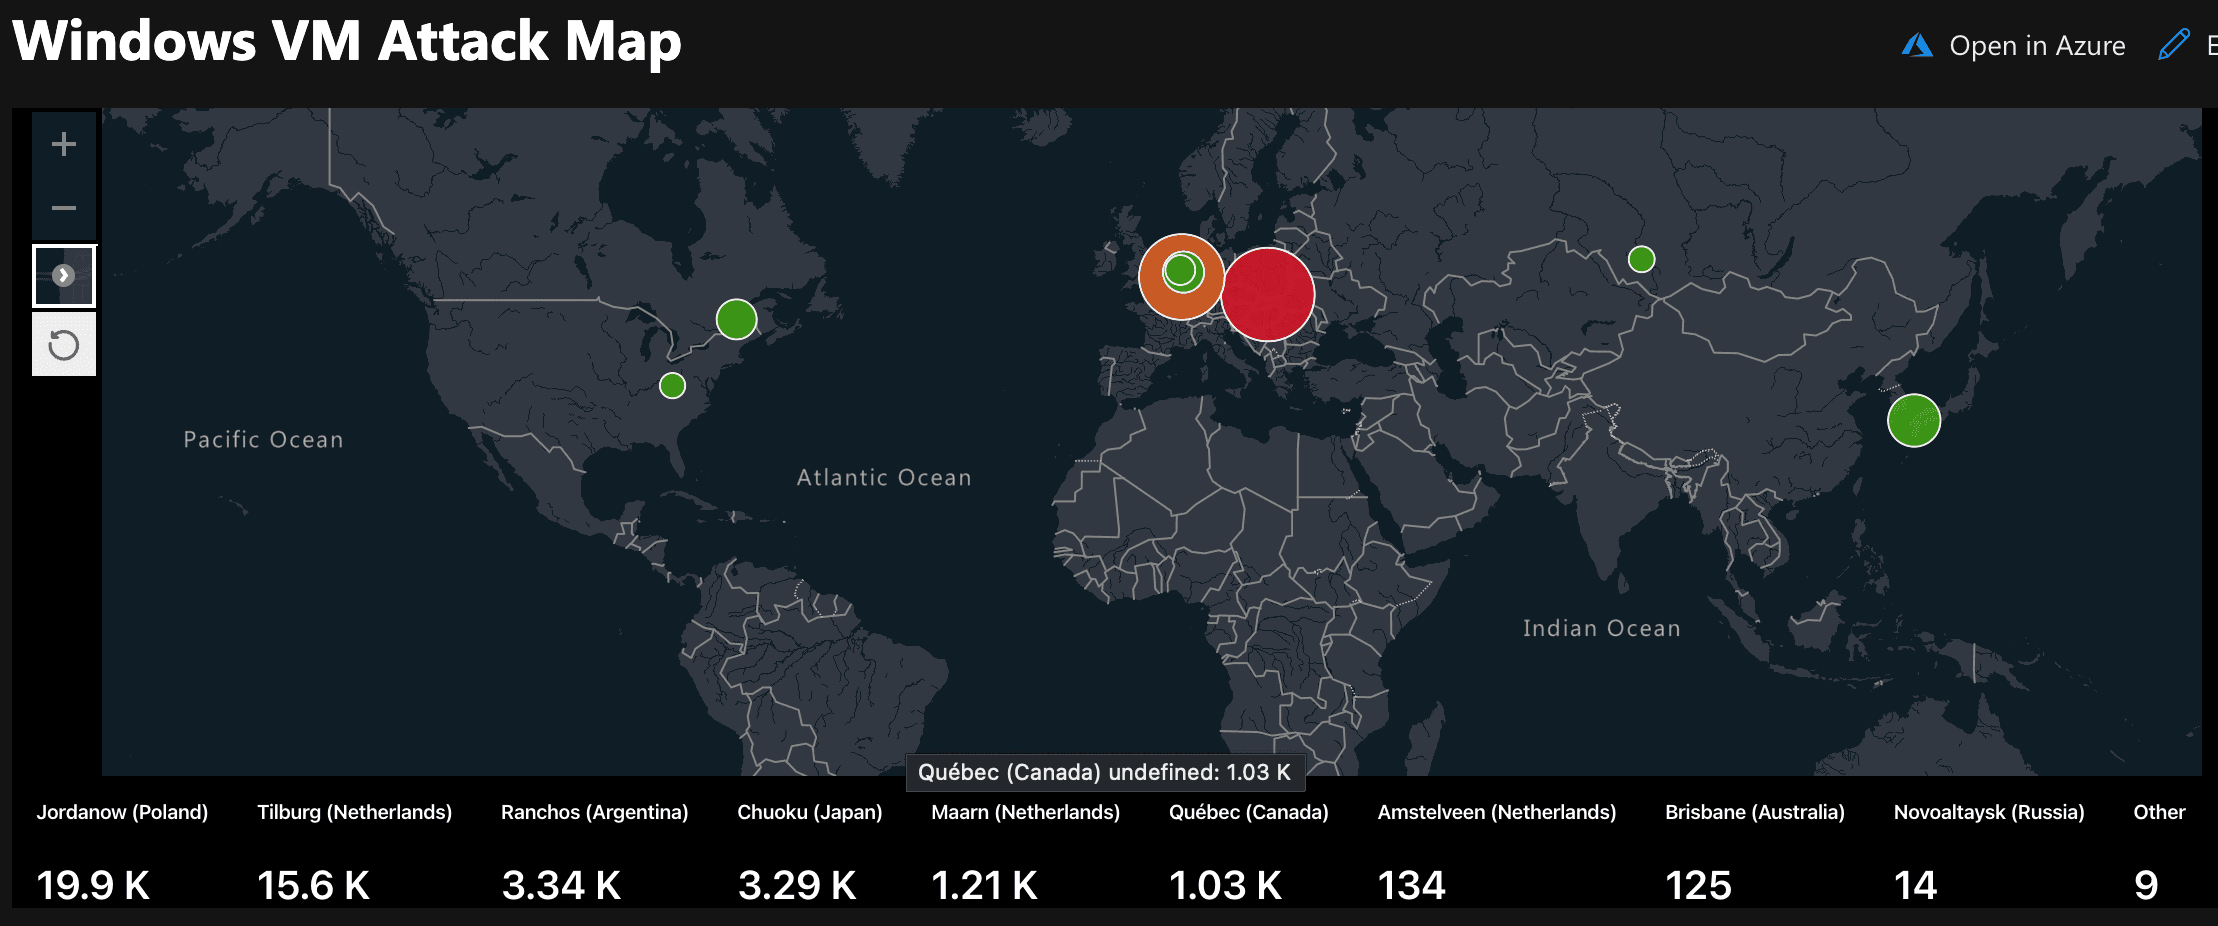
Cloud SOC Honeypot: Microsoft Sentinel Attack Map (Azure)

Cloud SOC Honeypot: Microsoft Sentinel Attack Map (Azure)

Built a cloud-based SOC lab: deployed a Windows honeypot VM in Azure, captured 44,000+ brute-force attempts, forwarded logs to Log Analytics, integrated with Microsoft Sentinel, enriched attacker IPs with GeoIP, and visualized global attack sources on a live map.
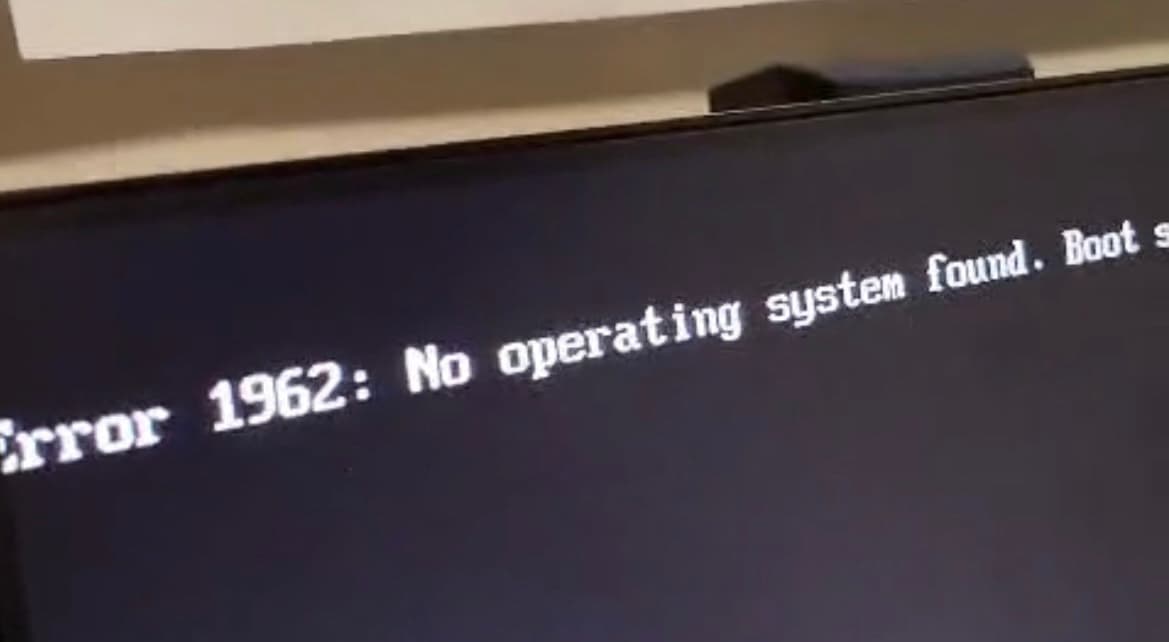
Windows Recovery Project: BIOS Boot Failure (Error 1962)

Windows Recovery Project: BIOS Boot Failure (Error 1962)

Troubleshot and restored a compromised Windows desktop that failed with BIOS Error 1962: 'No Operating System Found.' Adjusted BIOS boot configuration, attempted DISM/SFC repairs, then performed a clean OS reinstall via bootable USB to recover full functionality.
IntelliPath AI: Personalized Learning Through AI-Driven Video Summaries

IntelliPath AI: Personalized Learning Through AI-Driven Video Summaries

Developing an AI-powered platform that transforms YouTube videos into structured summaries, actionable notes, and personalized learning paths. Features include transcript analysis, AI assistant chat, sidebar navigation with history/folders, payment integration, and cloud-based persistence.
Astray: Lost Kingdoms (Python Pixel RPG)

Astray: Lost Kingdoms (Python Pixel RPG)

Building a 16-bit RPG in Python using Pygame, featuring interactive menus, real-time cutscenes, object-oriented game logic, and a story-driven quest system. Demonstrates software development skills, creativity, and iterative project management.